
Ship to production with confidence
I audit your application before launch — secrets, dependencies, selected code patterns, Terraform and other IaC files, Dockerfiles, and container images you provide. Automated checks run locally or in your CI. You receive a coverage-aware report, prioritized remediation guidance, and a documented retest for the agreed scope.
or write directly: contact@aadsec.xyz
Local-first · No source-code upload to AADSec · No AI code sharing without prior consent
Your team deploys fast. Security debt piles up even faster.
Most teams don't lack scanners — they lack clear answers. Hundreds of dependency alerts, a wall of CI warnings, and one unanswered question: can we deploy on Friday without undue risk?
Secrets in your source files
Credentials committed in files can be exposed. Git history scanning is an explicit option (--history) and can be partial on shallow clones.
Dependency alerts need context
Automated alerts do not all require the same treatment. Coverage and business context determine the next step.
AI-generated code merged without security review
Injection flaws and architectural weaknesses can slip past standard code reviews.
Infrastructure as Code (IaC) misconfigurations
Permissive cloud settings and public buckets can make it to production undetected.
Container and IAM weaknesses
Dockerfile misconfigurations, vulnerable base images and over-permissive IAM can widen the impact of a single flaw.
A focused audit, ready in 5 days
Scope definition
Repositories, cloud environments, and staging environments are agreed upon with written authorization.
Local, isolated execution
Proven tools run on your machine or in your CI with read-only access. Your code stays with you.
Human, contextual triage
I review findings in context and tell you what is confirmed, what needs checking, and what is outside the agreed scope.
Remediation plan and retest
After you apply fixes, I re-run the same checks on the corrected code and compare the results with the first report for the agreed scope. Each item is marked "not detected in this retest", "still detected", "not evaluated" or "indeterminate". The comparison is manual; it does not guarantee that no other vulnerability exists.
Verifiable security, not blind trust
Confidentiality is built into the process, not left to a promise.
Local or CI-based execution
No source code is uploaded to AADSec. Scanners run in your environment or CI; some scanner databases may be updated unless offline mode is used with a preloaded database.
Human review on your terms
Automated scans run in your environment, with no source-code upload to AADSec. Human review uses results you approve for sharing and, when needed, a scoped screen-sharing session. Any additional access is optional and requires your written agreement.
No source code retained
Audit reports are retained only as needed and deleted on request.
No transfer to third-party AI models
Your intellectual property is never sent to an LLM without your express consent.
Human validation of critical findings
Critical and high findings in the agreed scope are reviewed by me; automated results are not treated as final conclusions.
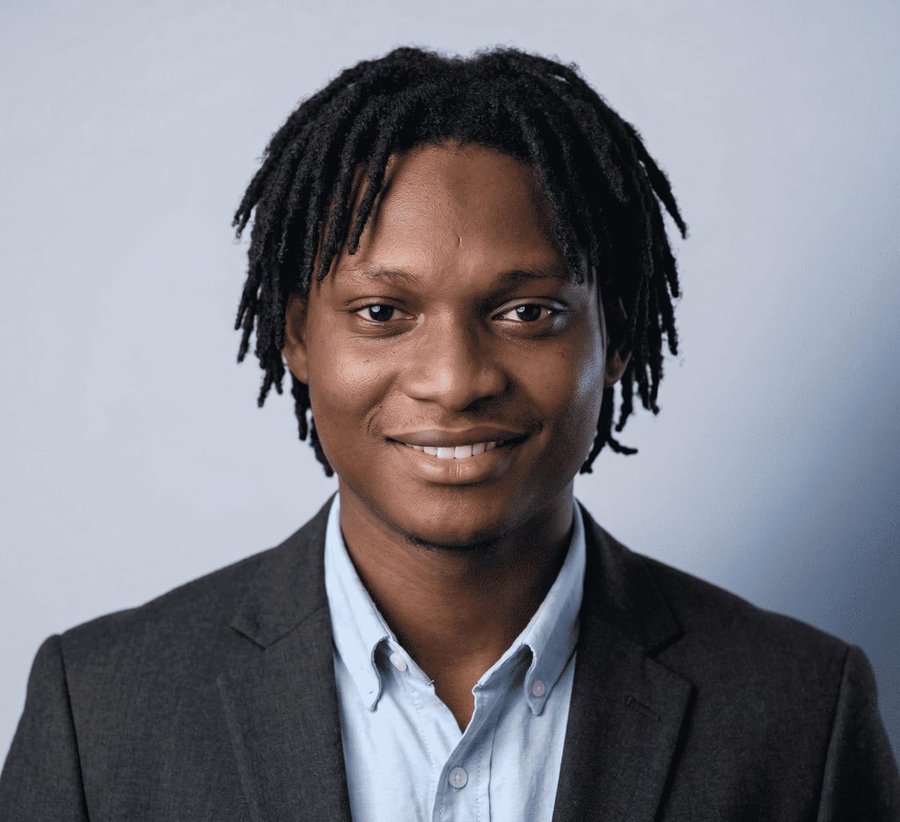
A real person behind every report
I'm Abdoul Aziz Dieng, a software engineer and DevSecOps consultant based in Dakar, working with teams internationally. Google Cybersecurity certified, I design and secure cloud architectures and CI/CD pipelines on AWS. Critical and high findings in the agreed scope are reviewed by me, not blindly accepted from automated scripts.
Google Cybersecurity Certified · AWS expertise · 50+ projects built · 10+ projects deployed
Beta program — 3 slots open
Reduced rates in exchange for detailed feedback and a testimonial.
Starter Repo Audit
$520 (beta)
- One repository
- SAST, SCA, secrets, IaC
- Automated checks available for the agreed stack and supplied files.
- Prioritized report (P0–P3) + 30-minute debrief session
- One retest included
Launch Security Audit
From $1,300 (beta)
- Scoped application review — areas agreed in writing
- SAST, SCA, secrets, IaC, containers
- Automated checks depend on the files, lockfiles and images supplied for the agreed scope.
- Optional passive DAST baseline on an authorised staging environment
- Full report + remediation plan + verification audit (retest)
DAST baseline is a separately scoped service. Target URL, staging environment, timing, crawl and request limits, and written authorisation are agreed before execution. It is not an active penetration test and is not part of the AADSec CLI.
Book a diagnosticAWS + AppSec Review
From $2,700 (beta)
- Scoped review of application areas, Terraform, IAM policies and delivery workflows agreed in writing
- Executive summary: release risk summary limited to the reviewed scope
- Prioritized remediation plan: concrete actions, owners, and timelines
Continuous
— from $149/monthAvailable after a first auditPost-audit monthly re-scan and triage for teams we've already audited. Keeps new findings under control.
This is what you receive
A report with an executive summary and technical findings: file, line, evidence, and recommended fix. See a sample report generated by AADSec on a deliberately vulnerable demo app.
AADSec Audit Report
Sample excerpt — deliberately vulnerable demo app
- Critical
Stripe access token committed in app/lib/crypto.js (line 19)
Secrets scanner · revoke and rotate the credential, then remove it from the code
- High
S3 bucket ACL allows public READ access (terraform/s3.tf, line 11)
IaC scanner · remove the public-read ACL and enable S3 Block Public Access
Generated on a deliberately vulnerable demo app — proof of format, not a client audit.
Practical security, without jargon or empty promises
AADSec isn't a magic tool and doesn't claim to replace a full, hands-on penetration test. My approach brings together proven open-source scanners. What you pay for is expert analysis: cutting through the noise, prioritizing what matters in the agreed scope, providing remediation guidance, and working with a dedicated person accountable for the quality of your report.
Shipping soon?
Don't find out about your vulnerabilities from your users — or worse, from an incident. Book a free 20-minute diagnostic: I'll look at your setup and tell you honestly whether an audit makes sense for you.
20 minutes, no commitment. No source-code upload to AADSec.